China Top Enterprise Access Control Suppliers?

China has become a major source of enterprise security technology, including biometric readers, smart cards, turnstiles, and cloud-managed access platforms. This guide examines China Top Enterprise Access Control Suppliers through practical business criteria, not promotional claims. It considers product reliability, integration capability, manufacturing experience, certification support, and after-sales service.

Enterprise Access Control systems protect offices, factories, campuses, data centers, and research facilities. A reliable supplier should explain how its readers perform in dusty entrances, crowded lobbies, and unstable network conditions. Buyers should also examine API documentation, device encryption, software updates, user capacity, and emergency procedures. Small details matter. A delayed door event can create operational confusion.

The suppliers discussed here represent different strengths. Some focus on large-scale hardware production. Others provide customized platforms for multinational companies or industrial sites. Their project histories, testing processes, and technical teams deserve careful review. However, supplier rankings are never permanent. Product lines change, support quality varies, and a successful pilot may not reflect every deployment environment.

Readers should request demonstration units, written service commitments, and clear ownership of system data. Independent testing and customer references can reveal weaknesses that brochures omit. Pricing also requires caution, because low initial costs may hide integration or maintenance expenses. This overview aims to support informed comparison while recognizing that every organization has different risks, budgets, and compliance requirements. Real evaluation takes time. That is often overlooked.

China Top Enterprise Access Control Suppliers?

Definition and Role of Access Control in Chinese Enterprises

Access control in Chinese enterprises is the structured process of deciding who may enter a place, use equipment, or reach digital resources. It combines identity verification, permission management, and activity records. A factory may use cards, facial verification, or mobile credentials at different gates. An office may restrict meeting rooms, server rooms, and laboratories. The purpose is not simply to lock doors. It is to connect people, roles, time, and risk.

Good access control supports daily operations and protects sensitive business information. Human resources can link permissions to job changes, while security teams review entry logs during an incident. A visitor might receive temporary access that expires after one afternoon. Contractors should reach only the areas required for their work. These details reduce accidental exposure and improve accountability. They also help enterprises manage large workforces across offices, warehouses, and production sites.

Still, no system is flawless. A lost badge, poorly reviewed permission, or shared account can weaken strong technology. That matters. Experienced administrators should audit access regularly and remove unused privileges. They should also provide clear alternatives when verification fails, especially during network outages or shift changes. Practical control is sometimes less convenient, but excessive restrictions may encourage unsafe workarounds. Chinese enterprises need security that fits real workflows, not merely impressive equipment.

China Top Enterprise Access Control Suppliers? - Definition and Role of Access Control in Chinese Enterprises

Access Control Dimension Definition Role in Chinese Enterprises Typical Application Key Security Benefit Relevant Requirement or Practice Recommended Performance Indicator
Identity Management Processes for creating, verifying, maintaining, and removing user, administrator, service, and device identities. Creates a reliable identity foundation for employees, contractors, partners, and connected devices. Employee onboarding, department transfers, resignations, supplier access, and service-account management. Reduces orphaned accounts, duplicate identities, and unauthorized access. Use a documented identity lifecycle with approval, periodic review, suspension, and deletion procedures. Percentage of active accounts with an assigned owner; account deactivation time after termination.
Authentication Verification that a person, system, or device is the legitimate holder of an identity. Prevents unauthorized users from entering enterprise applications, networks, facilities, and data environments. Password authentication, certificates, one-time passwords, biometrics, and multi-factor authentication. Improves resistance to credential theft, phishing, and account takeover. Apply stronger authentication to administrators, remote access, sensitive systems, and high-value transactions. Multi-factor authentication coverage; failed-login rate; percentage of privileged accounts using phishing-resistant methods.
Authorization Rules that determine which resources an authenticated identity may access and which actions it may perform. Limits employees and systems to the data and functions required for their responsibilities. Role-based access, attribute-based access, application permissions, database privileges, and API authorization. Supports least privilege and reduces the impact of compromised accounts. Access rights should be based on job responsibility, business need, resource sensitivity, and operating context. Number of excessive privileges identified; percentage of access rights reviewed on schedule.
Role-Based Access Control A model in which permissions are assigned to job roles rather than directly to individual users whenever practical. Helps large enterprises standardize access across branches, departments, projects, and subsidiaries. Finance approval roles, human-resource roles, production-operation roles, and system-administration roles. Simplifies administration and improves consistency during personnel changes. Separate incompatible duties, such as request, approval, payment, and audit functions. Percentage of users assigned through approved roles; number of conflicting-role exceptions.
Privileged Access Management Controls and monitors accounts that can change configurations, access sensitive data, or manage security controls. Protects high-impact administrator accounts used in data centers, cloud platforms, databases, and operational systems. Time-limited elevation, approval workflows, credential vaulting, session recording, and emergency access. Limits administrative misuse and improves investigation of high-risk activities. Use separate administrator identities, approval-based elevation, strong authentication, and detailed activity logging. Percentage of privileged sessions recorded; average time to remove unnecessary elevated rights.
Physical Access Control Measures that restrict entry to buildings, rooms, equipment areas, and other physical locations. Protects servers, network equipment, production lines, laboratories, archives, and restricted offices. Access cards, biometric verification, visitor registration, turnstiles, guards, and surveillance integration. Reduces unauthorized entry, theft, tampering, and physical damage to information assets. Maintain visitor records, access permissions, alarm procedures, and access logs for restricted areas. Unauthorized-entry attempts; visitor-log completeness; average response time to access alarms.
Network Access Control Controls whether users and devices may connect to wired, wireless, remote, or segmented enterprise networks. Separates office, production, guest, supplier, and sensitive network environments. Device posture checks, network segmentation, remote-access gateways, and access policies based on identity and location. Restricts lateral movement after a device or account is compromised. Classify networks by risk and limit connectivity between information-technology and operational-technology environments. Percentage of managed devices meeting security requirements; number of unauthorized network connections blocked.
Data Access Control Rules governing access to data according to sensitivity, ownership, purpose, location, and permitted operations. Protects personal information, important data, trade secrets, financial records, and operational data. Database permissions, document access, data masking, field-level controls, download restrictions, and data-loss monitoring. Reduces unauthorized disclosure, excessive internal access, and improper data use. Apply data classification, purpose limitation, minimum necessary access, and traceable approval procedures. Percentage of sensitive datasets with defined owners; unauthorized download events; access-review completion rate.
Application and API Access Controls access to enterprise applications, microservices, interfaces, and automated business transactions. Protects digital platforms and prevents unauthorized calls between internal and external systems. Single sign-on, token-based authorization, API scopes, service identities, and transaction-level permissions. Reduces abuse of exposed interfaces and limits application-to-application privileges. Use short-lived credentials, explicit scopes, rate limits, input validation, and separate service accounts. Percentage of APIs with authenticated requests; expired-token rate; blocked unauthorized API calls.
Zero-Trust Access An approach that continuously evaluates identity, device, application, resource, and context instead of automatically trusting network location. Supports secure access for branch offices, remote workers, cloud workloads, suppliers, and mobile users. Continuous verification, micro-segmentation, adaptive policies, device compliance checks, and session risk evaluation. Reduces reliance on perimeter security and limits unauthorized movement across environments. Verify explicitly, use least privilege, and continuously assess access conditions throughout a session. Percentage of remote sessions subject to continuous evaluation; number of high-risk sessions automatically restricted.
Audit Logging and Accountability Recording access requests, approvals, authentication events, permission changes, and user activities. Provides evidence for security investigations, internal control, compliance reviews, and incident response. Centralized logs, administrator activity records, access reports, alert correlation, and tamper-resistant storage. Improves traceability and shortens the time required to identify abnormal access. Synchronize system time, protect log integrity, restrict log access, and define retention periods based on risk and requirements. Log coverage for critical systems; alert investigation time; percentage of logs successfully delivered to centralized storage.
Periodic Access Review A formal review that confirms whether existing permissions remain appropriate and necessary. Prevents access accumulation caused by transfers, temporary projects, promotions, and organizational changes. Quarterly reviews for sensitive systems, event-driven reviews after role changes, and annual reviews for standard systems. Detects excessive, unused, conflicting, or expired permissions. Require resource owners and line managers to approve, modify, or revoke access based on documented evidence. Review completion rate; average remediation time; percentage of dormant permissions removed.
Compliance and Governance Policies, responsibilities, controls, and evidence used to manage access risks and satisfy applicable obligations. Aligns access-control practices with enterprise risk management and China’s cybersecurity, data, and personal-information governance requirements. Security policies, classified-protection assessments, privacy impact reviews, supplier assessments, and audit evidence. Improves regulatory readiness and establishes consistent accountability across business units. Common reference areas include the Cybersecurity Law, Data Security Law, Personal Information Protection Law, and classified protection practices such as MLPS 2.0. Number of unresolved access-control findings; policy review frequency; percentage of critical systems with assigned control owners.
Supplier and Third-Party Access Controls access granted to contractors, service providers, delivery partners, and other external organizations. Allows necessary collaboration while limiting risks introduced through external accounts and remote maintenance. Named accounts, contract-based permissions, approval workflows, time-limited access, monitored sessions, and automatic expiry. Reduces third-party exposure and improves accountability for outsourced operations. Grant only task-specific access, prohibit shared accounts where possible, and revoke access when work is completed or contracts end. Percentage of third-party accounts with expiry dates; vendor access review completion rate; number of shared external accounts.
Business Continuity and Emergency Access Procedures that maintain essential operations while controlling access during outages, disasters, or urgent incidents. Balances availability and security when normal identity services or approval channels are unavailable. Break-glass accounts, offline procedures, backup authentication, emergency approvals, and post-event reviews. Maintains critical services without creating permanent uncontrolled privileges. Keep emergency credentials protected, restrict their use, alert on activation, and review every emergency session afterward. Emergency-account activation count; time to restore critical access; percentage of emergency events reviewed.

Key Technologies Used by China’s Access Control Suppliers

China Top Enterprise Access Control Suppliers

China’s leading access control suppliers are investing heavily in connected security technologies. RFID cards and NFC credentials remain practical for offices, factories, and apartment buildings. Mobile credentials add convenience, especially when staff already use managed smartphones. However, lost phones still create a real administrative concern.

Biometric recognition is also advancing. Fingerprint readers work well in controlled indoor areas. Facial recognition can improve speed at busy entrances, but accuracy depends on lighting, camera position, and database quality. Reliable suppliers combine liveness detection with encrypted templates. This reduces spoofing risks and limits unnecessary exposure of personal data. No system is perfect. Poor enrollment can still cause frustrating failures.

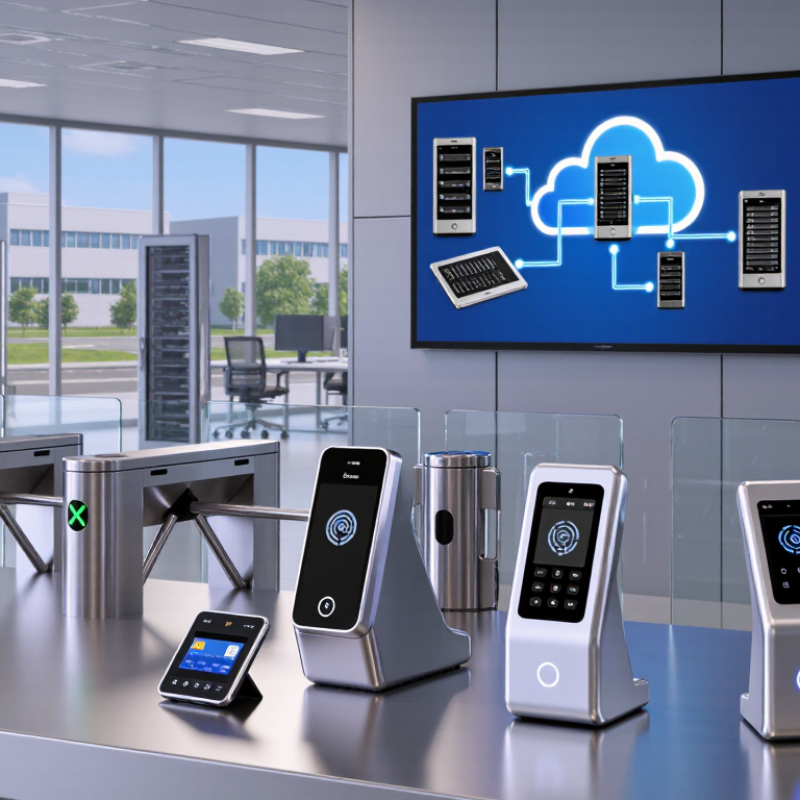
Edge computing is becoming more important. Local devices can verify credentials without sending every event to a distant server. This supports faster decisions and continued operation during network interruptions. Secure controllers commonly use encrypted communication, role-based permissions, tamper alerts, and audit logs. Power over Ethernet can simplify installation, while RS-485 remains useful for stable device connections. Cloud platforms help administrators manage multiple sites, review access records, and update policies remotely. Yet, integration often needs careful testing. A reader may work correctly alone but fail after connection with an older turnstile or management platform. Experienced suppliers should provide compatibility checks, clear documentation, firmware controls, and realistic on-site trials before large deployment.

Leading Enterprise Access Control Suppliers in China

Leading Enterprise Access Control Suppliers in China

Leading enterprise access control suppliers in China serve offices, factories, campuses, hospitals, and logistics facilities. Their solutions commonly include smart controllers, card readers, biometric terminals, visitor management, and cloud-based administration. Experienced suppliers should explain how each device performs in real conditions, not only present attractive specifications.

A reliable supplier can provide wiring diagrams, testing procedures, installation guidance, and maintenance training. Ask about encryption, user permissions, audit trails, emergency exit functions, and data retention settings. These details matter when hundreds of employees enter through several doors each morning. Strong suppliers also support system integration with attendance, video monitoring, elevators, and human resources platforms.

Look beyond the lowest quotation. It may exclude software updates, replacement parts, or on-site assistance. Request sample hardware and test it with your existing network. Small delays become expensive when access fails during shift changes. Supplier certifications, documented quality controls, export experience, and responsive technical support can reveal professional maturity. No supplier is perfect. I have found that clear communication often matters as much as advanced hardware. A careful evaluation may still miss hidden installation problems, so maintain a practical contingency plan.

How to Evaluate Chinese Access Control System Providers

Evaluating Chinese access control providers requires more than comparing quotations.

Grand View Research estimated the global market near USD 10 billion in 2023, with about 8% annual growth through 2030. Growth widens supplier choice, but it does not prove dependable delivery.

Start with deployment evidence: door count, reader technology, network design, and failure response.

Ask for two comparable customer references, rather than polished case studies. Inspect a live installation if practical.

Technical due diligence should test interoperability and resilience.

Check OSDP support, Wiegand migration, REST APIs, and standard identity directories. Request penetration-test summaries, firmware policies, encryption details, and data-retention controls.

The 2024 Verizon Data Breach Investigations Report recorded a 180% rise in vulnerability exploitation.

Access controllers deserve the same scrutiny as servers.

Disconnect a controller during testing. Then measure event recovery and offline access.

Small tests expose expensive weaknesses.

Supplier quality also depends on execution.

Review ISO 9001 evidence, traceability records, factory tests, spare-parts plans, and escalation contacts. Ask whether local technicians can meet the contracted response window. Verify regional certifications independently; current certificates may still omit installation-specific requirements.

A low quotation can conceal licensing, cloud fees, replacement readers, or retraining.

I have made that mistake.

Score security, lifecycle cost, integration, service, and documented evidence. Leave room for doubt.

Applications and Industry Trends in Enterprise Access Control

Enterprise access control in China is moving beyond simple badge entry. Offices now combine smart cards, mobile credentials, visitor kiosks, and elevator controls. A guest may receive a temporary code at reception, while employees use encrypted credentials on managed phones. Manufacturing sites need stricter zone control. Production doors can connect with time schedules, safety procedures, and attendance records. Hospitals and campuses also separate public, staff, and restricted areas.

Cloud management is becoming common among large organizations with multiple locations. Administrators can change permissions from one control center and review entry events within seconds. Edge processing remains important when networks are unstable. Local controllers can continue operating during short outages, then synchronize records later. Chinese suppliers are also improving integration with video monitoring, alarms, human-resource systems, and building platforms. The practical value is clear: fewer isolated systems and faster incident review.

Biometric verification is expanding, but adoption is not automatic. Privacy expectations, data storage, lighting, masks, and user consent require careful planning. No system is flawless. A fingerprint reader may struggle with wet hands, while mobile access depends on battery life and device management. Reliable projects therefore include fallback credentials, audit trails, maintenance testing, and clear staff training. Procurement teams should assess cybersecurity updates, support capability, compatibility, and total operating cost rather than choosing hardware by appearance alone.

Cart Summary

Subtotal: $0